
Blog
Ideas and insights on AI security, governance and agents.
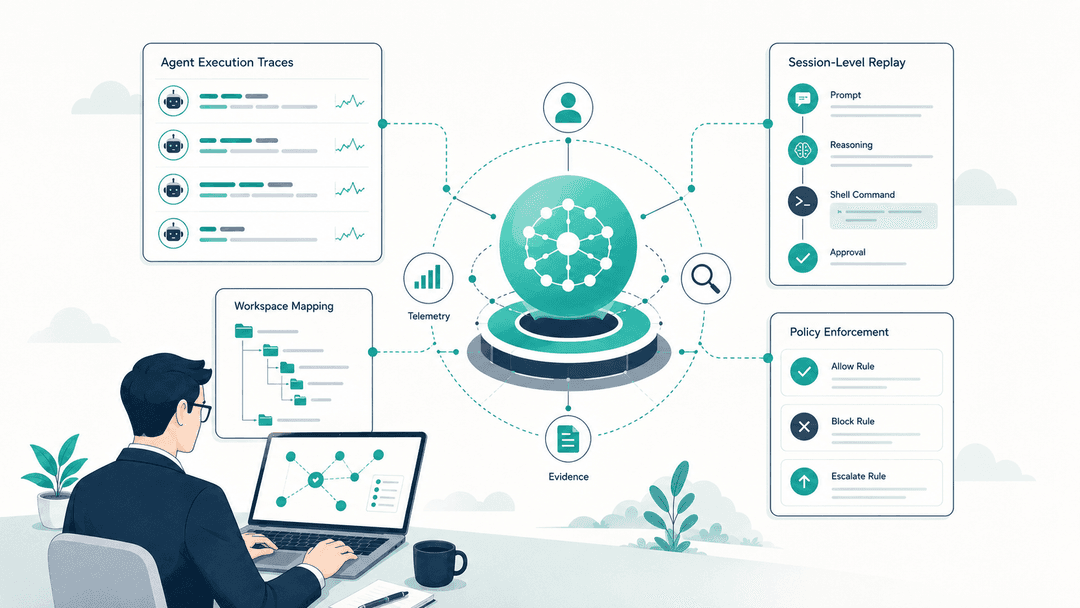
Inside the Agent Control Plane: What Full Agent Visibility Actually Looks Like
A walkthrough of what KonaSense sees when AI coding agents run across your org: execution traces, session-level replay, workspace mapping, and policy enforcement.
JUL 05, 2026 · 5 minRead article →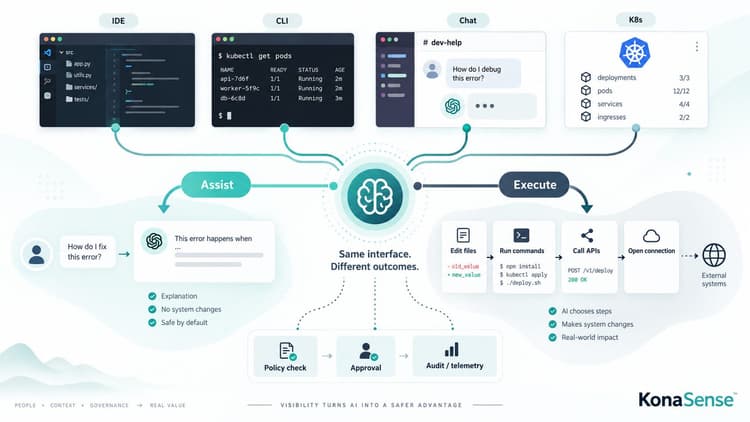
When AI Starts Executing: The Label on the Tool Won't Tell You the Risk
An IDE, a CLI, a workload in Kubernetes, none of those labels tells you how much an AI system can do. Here is the question that does, and how to govern it
AI SECURITY / SEP 27, 2026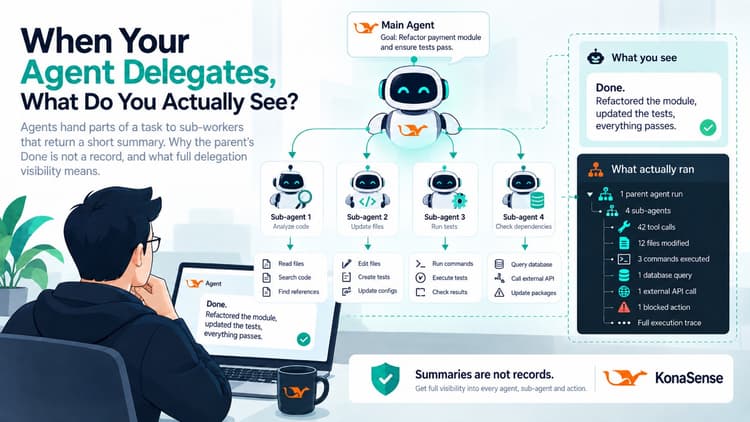
When Your Agent Delegates, What Do You Actually See?
Agents hand parts of a task to sub-workers that return a short summary. Why the parent's Done is not a record, and what full delegation visibility means
AI SECURITY / SEP 27, 2026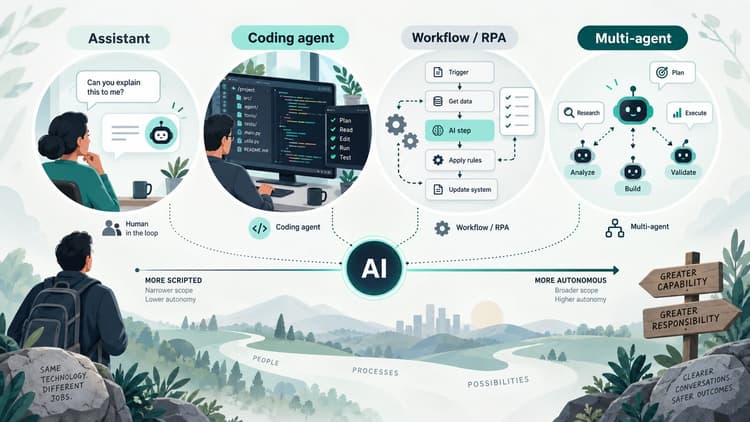
Agent, Bot, or Just Software? What People Actually Mean by AI Agent
There is no settled definition of an AI agent. Here is the lineage from bots and RPA, a working definition, the types you will meet, and how one actually runs
AI SECURITY / SEP 27, 2026
Prompt Injection Is a Supply-Chain Problem Now
When an agent reads a web page, a ticket, or a tool result, untrusted content can hijack its next action. Why indirect prompt injection is a supply-chain risk for agents
AI SECURITY / SEP 27, 2026
The Tool Call Is the New Perimeter: Governing MCP for AI Agents
Your agents are talking to tools you have never inventoried. Here is what MCP is, why it is a blind spot, and what it means to govern a tool call before it runs
PRODUCT / AUG 25, 2026
Observability and Governance for AI Apps on Company Desktops
See and govern Claude Code, Cowork, Codex and ChatGPT Work on employee desktops, with the same policies and incident queue, using telemetry they already emit
AI SECURITY / JUL 05, 2026
What Is an AI Agent, Actually? The Word Got Stretched, and That's Now a Governance Problem
Every vendor calls their product an agent. The technical definition is narrower than the marketing, and the gap between the two is where governance breaks.
AI SECURITY / MAY 26, 2026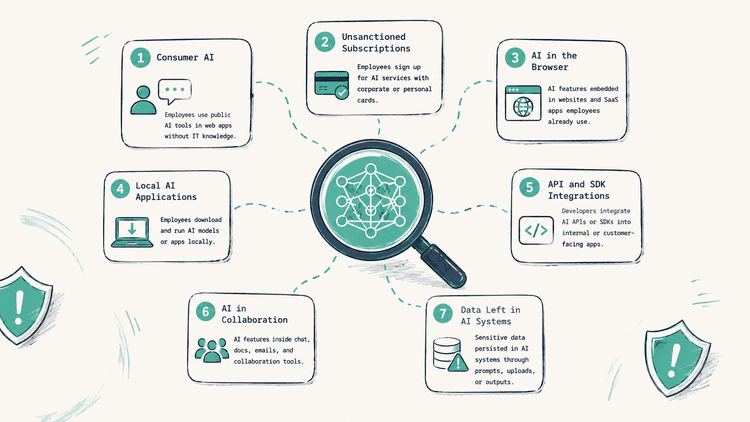
The seven types of Shadow AI legacy DLP usually misses
Shadow AI is not one problem, it is seven. Here is the taxonomy KonaSense uses to classify every incident, and why most legacy DLP deployments were not built to model them.
ENGINEERING / MAY 25, 2026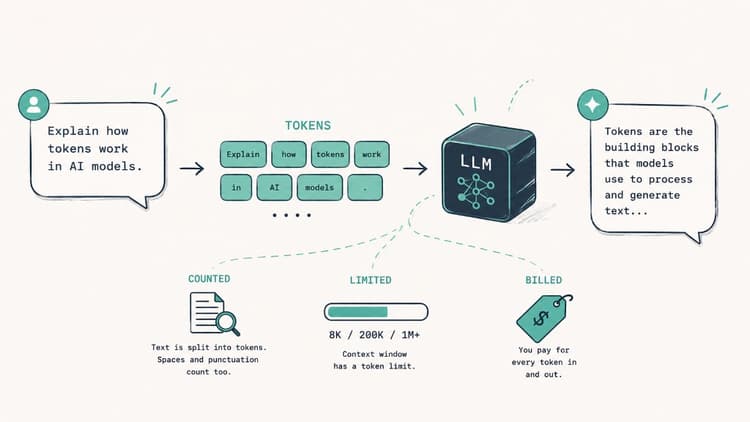
What is a token in AI, how it is counted, and why you pay for every one
A technical guide to tokens in LLMs: what they are, how BPE splits text, why both request and response are billed, and how to estimate real cost in 2026.
AI SECURITY / MAY 11, 2026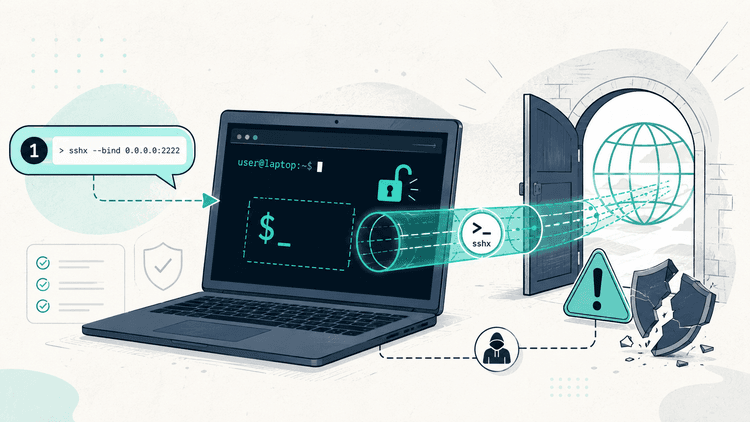
One Prompt, One Unauthenticated Shell on Your Laptop, Open to the Internet
Series · Agent Control Plane: AI Real Risks · Part 3 of ∞
AI SECURITY / MAY 07, 2026
AI Policies Your Auditor Will Actually Accept: A Free Generator for the Five You Need in 2026
Most companies in 2026 do not have an AI policy. The ones that do have one generic template pulled off the internet that does not mention their industry, their jurisdiction, or how they actually use...
AI SECURITY / MAY 06, 2026
Your Coding Agent Just Opened an End-to-End Encrypted P2P Tunnel Out of Your Network
In Part 1 we showed Claude Code stand up a Cloudflare quick tunnel in 37 seconds. The data sat on the laptop. A door opened to it. Part 2 is the inverse directi
AI SECURITY / MAY 06, 2026
What Is an Agent Control Plane, and Why Does Every Enterprise Need One
Forrester named the category in December 2025. Five months later it is the most contested layer in the enterprise AI stack. Here is what an Agent Control Plane actually is, what it must do, and where KonaSense fits.
AI SECURITY / APR 23, 2026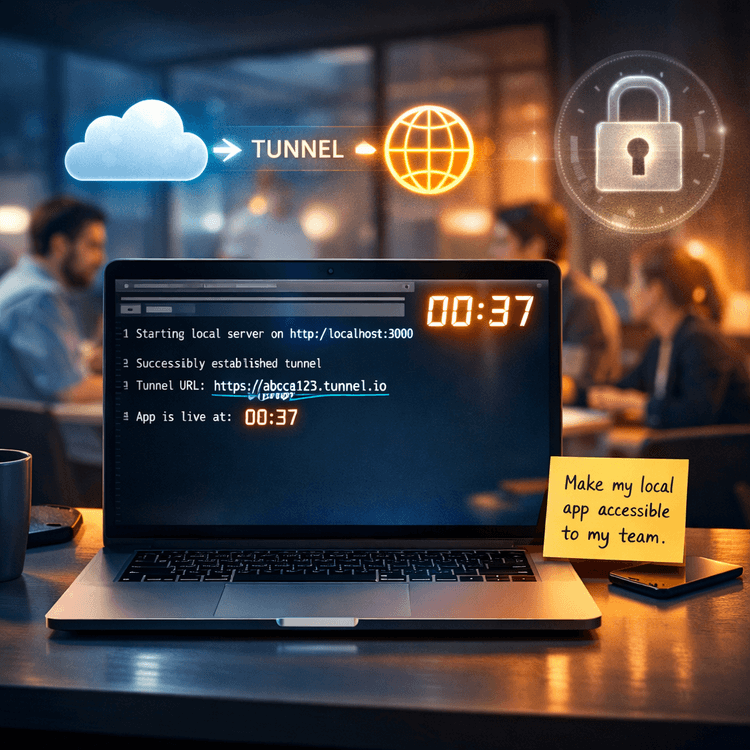
Everyone Is a Developer Now, and Something in Your Company Is About to Leak
AI coding tools turned every knowledge worker into a developer. The monitoring stack you bought in 2020 was not designed to see what happens next.
AI SECURITY / APR 20, 2026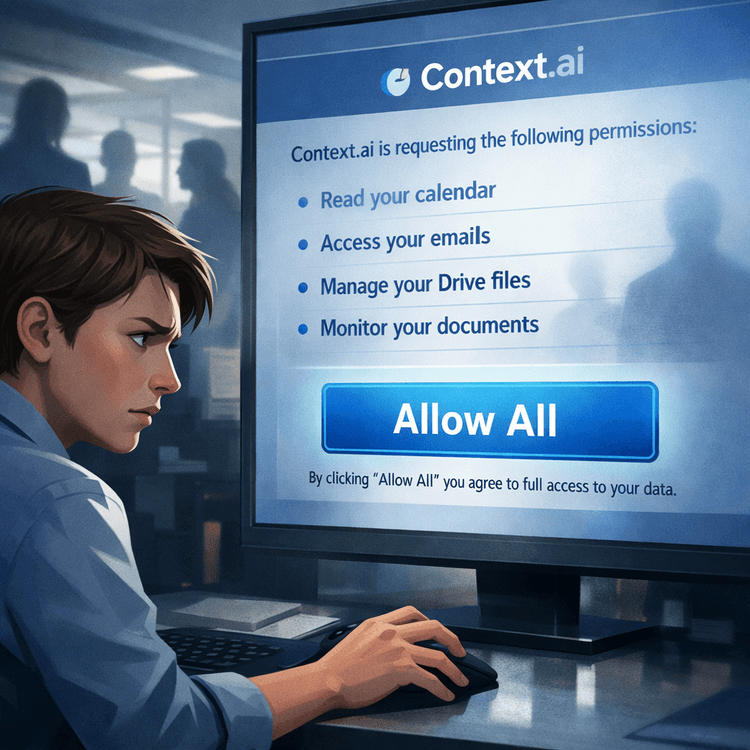
Your security team has never seen the apps breaching you
Explore the risks of broad OAuth permissions in AI tools, highlighted by the Vercel breach, and learn essential steps to safeguard your accounts.
SHADOW AI RISK / MAR 10, 2026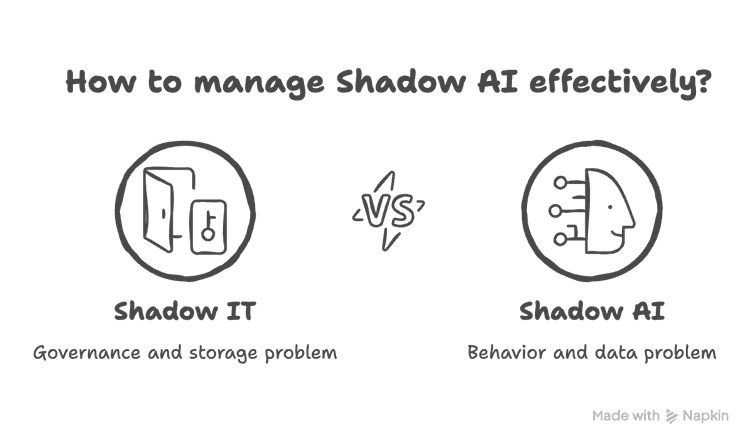
What Is Shadow AI: And Why It Is Nothing Like Shadow IT
Shadow AI is not shadow IT. It is a faster, broader, and more invisible category of risk that the 2020 governance stack was not designed to see.
ENTERPRISE AI GOVERNANCE / FEB 24, 2026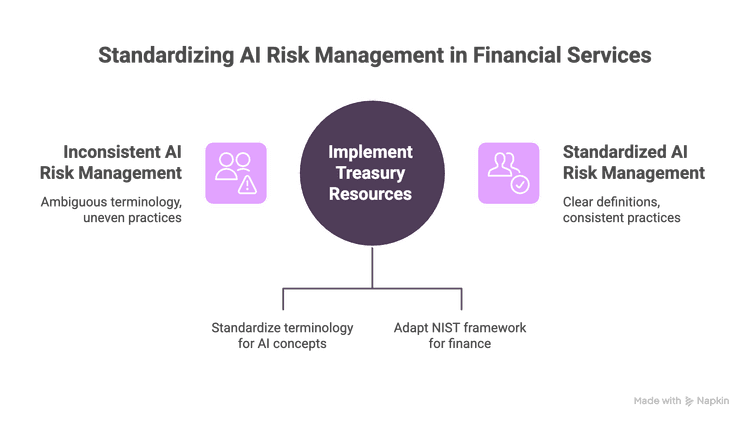
Treasury just raised the bar on AI risk. Here is the practical playbook.
What the new Treasury guidance on AI risk actually requires, and a practical playbook for security and compliance leaders implementing it this quarter.
AI AGENTS / FEB 24, 2026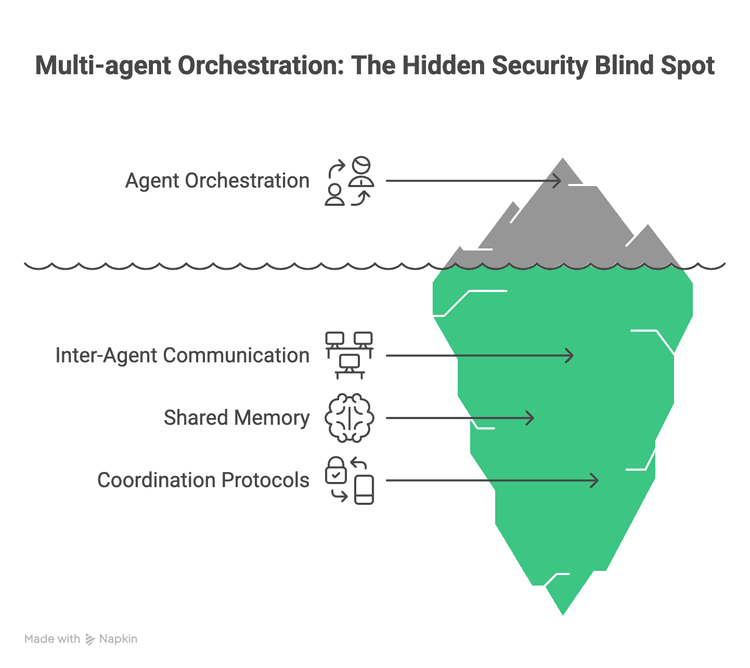
Multi agent orchestration is the next blind spot
When agents call agents call tools, the audit trail breaks. Why multi-agent orchestration is the next visibility gap for security teams.
SHADOW AI RISK / FEB 18, 2026
Shadow AI: Identifying and Mitigating Your Organization's Invisible Risk
A practical guide for security leaders on detecting and reducing the invisible risk surface created by unsanctioned AI tool usage across the workforce.
ENTERPRISE AI GOVERNANCE / FEB 18, 2026
KonaSense: People-first AI security for the real world
Why AI security has to start with the people using AI every day, not the models. The thinking behind the KonaSense platform and what we are building.